TimeLeaf works with Microsoft 365 in four ways: employees sign in with their Microsoft account, employees are imported from Microsoft Entra ID, the TimeLeaf bot sends approvals and notifications in Microsoft Teams, and approved leave appears on Outlook calendars.
What you need
| Part | Plan | Microsoft rights |
|---|---|---|
| Sign in with Microsoft (single sign-on) | Professional and above | Someone who can create an app registration in Microsoft Entra ID and grant admin consent |
| Directory sync | Professional and above | Admin consent for directory read permissions |
| TimeLeaf bot in Teams | Every plan | Someone who can allow or install Teams apps for your organisation |
| Shared company calendar | Professional and above | Admin consent for an application calendar permission |
| Employees' own Outlook calendars | Professional and above (uses the sign-in app) | Admin consent for a delegated calendar permission |
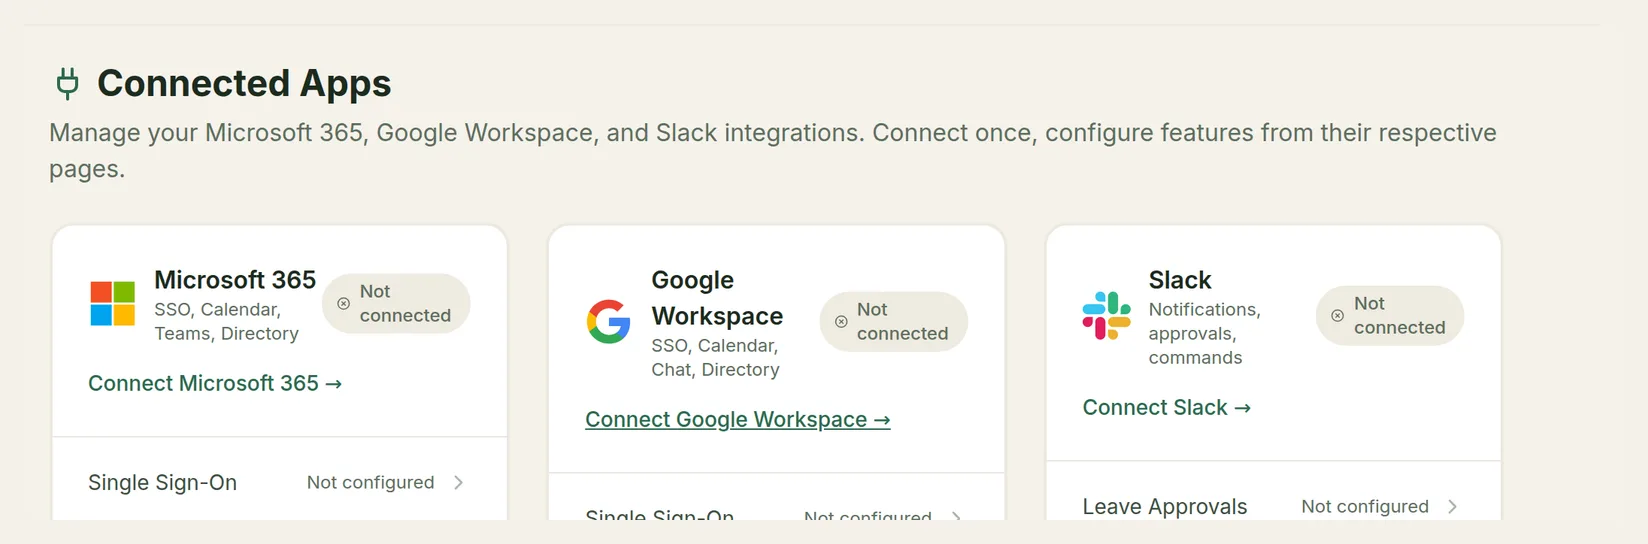
You also need to be a TimeLeaf admin. Integrations › Connected Apps shows the Microsoft 365 card with the status of each part and a link to its settings page.
Set up sign-in with Microsoft
Microsoft sign-in is the base for directory sync and calendar sync, so set it up first.
Register an app in Microsoft Entra ID
In the Azure portal, go to Microsoft Entra ID › App registrations › New registration. Give it a name (for example "TimeLeaf"), choose Single tenant (accounts in your organisation only) and click Register. On the Overview page, copy the Application (client) ID and the Directory (tenant) ID.
Create a client secret
Go to Certificates & secrets › New client secret, choose an expiry and click Add. Copy the secret's Value straight away; Azure shows it only once.
Add the provider in TimeLeaf
In TimeLeaf, go to Integrations › Single Sign-On and click Add Provider. Choose Microsoft Entra ID (Azure AD) as the Provider Type and fill in a Display Name, the Client ID, the Client Secret, the Tenant ID (the directory ID, not "common") and your Email Domain. Tick Set as active provider and save.
Add the redirect URIs in Azure
Open the saved provider with Edit to see its Redirect URIs and copy both. In Azure, go to Authentication › Add a platform › Web and add both URIs. They look like:
https://<your-workspace>.timeleaf.io/api/auth/sso/callback/<provider id>(sign-in)https://<your-workspace>.timeleaf.io/api/me/calendar/callback(employees' own calendars)
Check the permissions
In Azure, go to API permissions. Add only what you use (all Microsoft Graph), then click Grant admin consent:
| Permission | Type | Needed for |
|---|---|---|
User.Read | Delegated | Sign-in (present by default) |
User.Read.All (or User.ReadBasic.All) | Application | Directory search, sync and org chart |
Calendars.ReadWrite | Delegated | Employees connecting their own Outlook calendar |
Calendars.ReadWrite | Application | Only the shared company calendar |
MailboxSettings.Read | Application | Seeing who has an out-of-office reply on |
The application Calendars.ReadWrite permission reaches every calendar in your organisation on its own. A Microsoft 365 admin can limit it to the one shared calendar mailbox with Exchange Online's role-based access control for applications; the Single Sign-On page explains how.
Test it
Sign out and use "Sign in with Microsoft" on the sign-in page.
To require everyone to use Microsoft sign-in, and to set roles from Entra groups, see Single Sign-On.
Import employees from Entra ID
Go to People › Employees & Teams and click Sync Directory. The first time, TimeLeaf asks you to add one more redirect URI in Azure and grant admin consent for the directory permissions. TimeLeaf imports enabled users (not disabled accounts, room or equipment mailboxes, or guests), syncs again every day, and archives people who leave. The full guide is Directory Sync.
The TimeLeaf bot in Microsoft Teams
Teams uses the TimeLeaf app from the Microsoft Teams Store. TimeLeaf runs the bot, so there is nothing to set up in Azure for it, and it works on every plan.
Install the app
Install TimeLeaf from the Microsoft Teams app catalog (allow it in the Teams admin center if your organisation restricts apps). Integrations › Messengers › Microsoft Teams shows this as the next step.
Install the bot for everyone (optional)
So that people get messages without opening the bot first, click Grant admin consent on Integrations › Messengers › Microsoft Teams and approve on Microsoft's page with a Microsoft 365 admin account. This needs Microsoft sign-in set up with your Directory (tenant) ID first. TimeLeaf then installs the bot for everyone who can sign in, in batches in the background, and the same page shows progress. Install for everyone again picks up people added since.
Each employee links their account
Each person does this once. In the TimeLeaf bot in Teams, they tap Sign in to TimeLeaf and sign in. On Connect Microsoft Teams they click Get my code and send the pair … message it shows to the bot. The code works once and expires in 10 minutes. Send it only in your own chat with the bot, never share it.
The bot sends:
- Leave requests to approvers, with approve and decline buttons, and decisions and cancellations to the employee.
- Submitted timesheets to approvers, and decisions to the employee.
- Shift assignments, on-call handoffs and overtime opportunities.
- A "still working?" prompt to someone who forgot to clock out.
- Approval cards for changes an AI assistant proposes (see AI Copilot).
Employees can also type commands to the bot, such as check (balances), request (book leave), clockin, clockout, whosout, schedule, timesheet and pending. Type help for the list your plan includes.
Post to a Teams channel (optional)
To post to a channel instead of direct messages, click Add Teams Config on Integrations › Messengers › Microsoft Teams, choose Channel Webhook and paste the channel's incoming webhook URL. You can also tick Post a daily "who's out today" digest to this channel and choose a Post time (company time zone). The digest names who is out and whether for all or part of the day, never the leave type.
Approved leave on Outlook calendars
Go to Integrations › Calendar Sync.
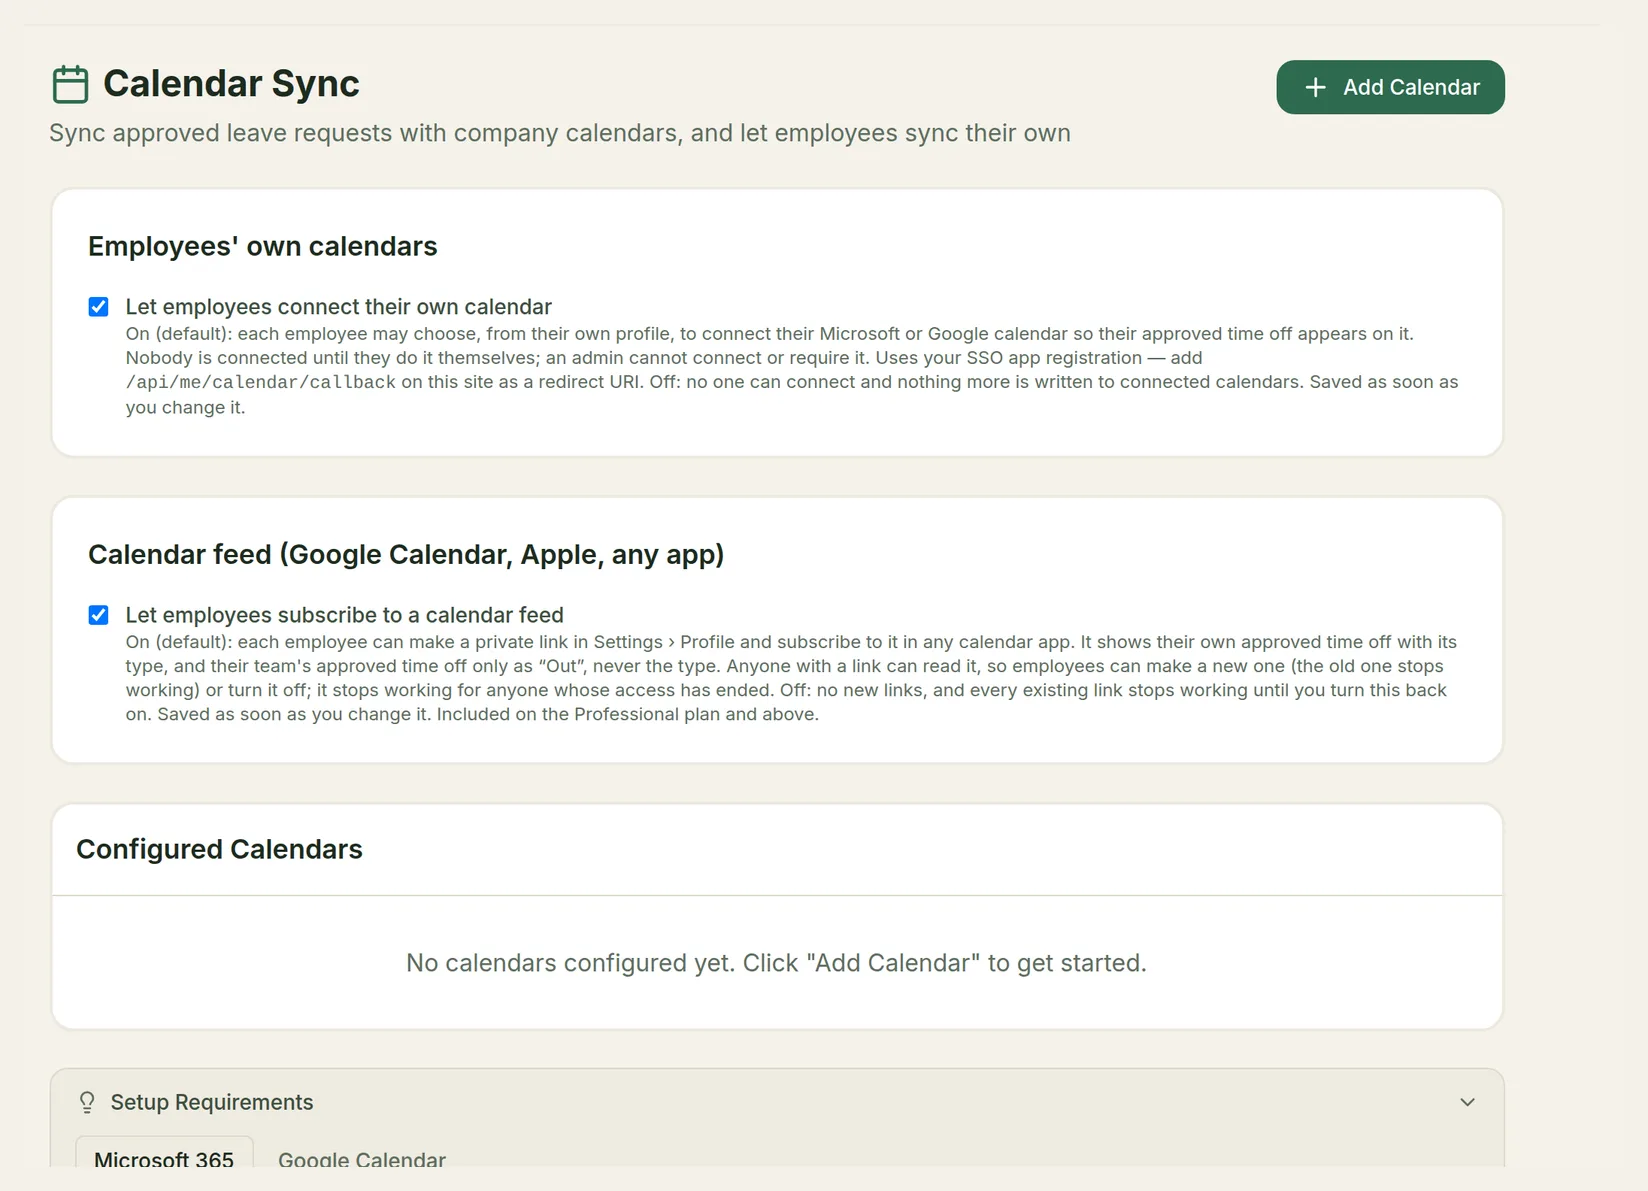
- Employees' own calendars. With Let employees connect their own calendar on (the default), each employee can connect their Outlook calendar from their own Settings › Profile, and their approved time off is added to it. Nobody is connected until they do it themselves. It needs the delegated
Calendars.ReadWritepermission and the calendar redirect URI from step 4 above. - A shared company calendar (Professional and above). Click Add Calendar, give it a Configuration Name, choose Microsoft 365 / Outlook, enter the Calendar Owner Email (a shared or resource mailbox), use Discover Calendars to pick the Calendar ID, and choose whether to Sync approved requests and Sync pending requests (tentative). Approved leave is added as all-day events shown as out of office, named with the person and the leave type. It needs the application
Calendars.ReadWritepermission. - Calendar feed. With Let employees subscribe to a calendar feed on, each employee can make a private link under Settings › Profile to subscribe from any calendar app.
Troubleshooting
| Problem | What to do |
|---|---|
| Sign-in fails with a redirect error | The redirect URI in Azure must match the one on the provider's Redirect URIs exactly, including https:// and the provider id at the end. |
| The Tenant ID field turns red | Enter your directory's Tenant ID (a GUID) from Microsoft Entra ID. common and organizations are refused because they would let any Microsoft directory sign in. |
| Sync Directory imports nobody | Check that admin consent was granted for User.Read.All (or User.ReadBasic.All) as an Application permission, and that the provider is active. |
| Directory sync says the client secret is invalid | The secret expired. Create a new one in Azure and paste it with Update Client Secret on People › Employees & Teams. |
| Grant admin consent for Teams asks you to set up sign-in first | Add Microsoft Entra ID sign-in with your Directory (tenant) ID under Integrations › Single Sign-On, then try again. |
| A person gets no Teams messages | They haven't linked their account yet (the pairing code), or the bot isn't installed for them. |
| Leave isn't appearing on a shared calendar | Check the application Calendars.ReadWrite permission has admin consent, the mailbox is in Exchange Online, and the configuration is Enabled. |